In containerized production environments, applications come and go, but data must endure. While Docker containers are inherently ephemeral and can be destroyed or rebuilt in seconds, your application state—ranging from PostgreSQL databases and Redis caches to uploaded media and LLM weights—lives inside persistent Docker volumes.
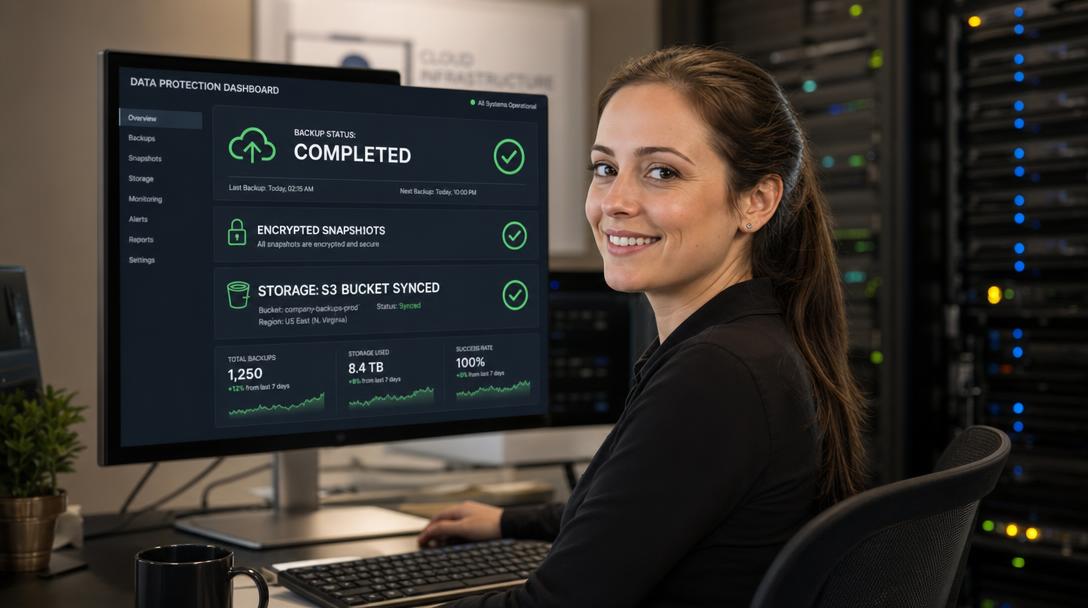
Too many system administrators rely on crude shell scripts running tar -czf to dump volumes. Traditional archive methods suffer from severe drawbacks: they lack client-side encryption, consume massive amounts of storage due to zero deduplication, offer no point-in-time snapshot pruning, and fail to verify backup integrity.
The modern, production-grade standard for container data protection is Restic. Restic is a fast, cryptographically secure backup program that delivers end-to-end encryption, content-defined chunk deduplication, and native S3 object storage integration. In this tutorial, you will learn how to design and automate an offsite Docker volume backup pipeline to any S3-compatible backend (AWS S3, MinIO, Wasabi, or Backblaze B2) using a dedicated, non-intrusive Docker container.
Why Restic is the Superior Choice for Docker Volumes
Compared to legacy tools like Duplicity, Borg, or raw tarballs, Restic provides specific technical features critical for container operations:
- Content-Defined Chunking: Rather than backing up entire multi-gigabyte files when a few bytes change, Restic uses Rabin fingerprints to split files into variable-length blobs. If 5 Docker volumes contain duplicate database libraries or static assets, Restic stores those chunks only once across the entire repository.
- Zero-Knowledge Cryptography: All data chunks, metadata, and directory trees are encrypted client-side using AES-256 in Galois/Counter Mode (GCM) and authenticated with Poly1305 before transmission over the network. Your storage provider never sees your plaintext data.
- Native S3 Protocol Support: No FUSE mounts or rsync daemons required. Restic communicates directly with AWS S3, MinIO, or Cloudflare R2 via standard HTTP/S S3 API primitives.
- Single Static Binary / Container: No complex runtime dependencies, Python interpreters, or shared C libraries to break across Linux distribution upgrades.
Technical Prerequisites
Before implementing the backup pipeline, ensure you have:
- Docker Host: A Linux server running Docker Engine 24.0+ and Docker Compose v2.
- Existing Docker Volumes: Named volumes or bind mounts you wish to protect (e.g., from your Open-WebUI stack or Caddy proxy certificates).
- S3-Compatible Storage: An S3 bucket created on AWS S3, MinIO, Wasabi, or Backblaze B2 along with an Access Key, Secret Key, and Bucket Name.
Step 1: Understanding Non-Intrusive Volume Backups
As detailed in the Docker Official Volume Documentation, the safest way to back up volume data without altering your running containers is to mount those volumes read-only (:ro) into an ephemeral or scheduled backup utility container.
By mounting target volumes with the :ro flag, the backup process can read active data blocks without the risk of accidentally modifying, locking, or corrupting files used by active application processes.
Step 2: Project Setup and Environment Configuration
Create a dedicated directory on your server for the backup orchestration stack:
mkdir -p ~/stacks/docker-backup && cd ~/stacks/docker-backupCreate a secure environment file named .env to house your S3 credentials and repository master password. Restrict its permissions so only root can read it:
# Restic Repository Configuration
RESTIC_REPOSITORY=s3:https://s3.eu-central-1.amazonaws.com/your-backup-bucket-name/docker-backups
RESTIC_PASSWORD=your_super_secure_master_restic_password_change_me

# S3 Credentials
AWS_ACCESS_KEY_ID=your_s3_access_key
AWS_SECRET_ACCESS_KEY=your_s3_secret_key

# Backup Retention Policy
KEEP_LAST=7
KEEP_DAILY=7
KEEP_WEEKLY=4
KEEP_MONTHLY=6
Step 3: Creating the Automated Backup Script
We will create an idempotent backup and maintenance script named backup.sh that initializes the repository if it does not exist, executes the snapshot, prunes old data according to our retention policy, and checks repository health.
#!/bin/sh
set -e

echo "Starting Docker volume backup with Restic..."

# 1. Initialize repository if not already initialized
if ! restic snapshots > /dev/null 2>&1; then
    echo "Initializing new Restic repository in S3..."
    restic init
fi

# 2. Execute snapshot of all mounted volumes
echo "Creating encrypted volume snapshot..."
restic backup /data \
    --tag "docker-volumes" \
    --tag "host-$(hostname)" \
    --exclude-caches \
    --verbose

# 3. Apply retention policy and prune unreferenced chunks
echo "Applying retention policy (forget & prune)..."
restic forget \
    --tag "docker-volumes" \
    --keep-last ${KEEP_LAST:-7} \
    --keep-daily ${KEEP_DAILY:-7} \
    --keep-weekly ${KEEP_WEEKLY:-4} \
    --keep-monthly ${KEEP_MONTHLY:-6} \
    --prune

# 4. Quick repository consistency check
echo "Verifying repository integrity..."
restic check --read-data-subset=5%

echo "Backup workflow successfully completed!"
Step 4: Crafting the Docker Compose Stack
Now, define the docker-compose.yml file. We mount the official Restic alpine container alongside target volumes, adhering to the Restic Official Documentation:
services:
  restic-backup:
    image: restic/restic:latest
    container_name: docker-volume-backup
    restart: unless-stopped
    env_file:
      - .env
    volumes:
      # Mount the automated backup script
      - ./backup.sh:/usr/local/bin/backup.sh:ro

      # Mount your target Docker volumes (READ-ONLY)
      - openwebui_data:/data/openwebui:ro
      - ollama_data:/data/ollama:ro
      - caddy_data:/data/caddy:ro

      # Persistent cache directory to accelerate hash computation
      - ./restic_cache:/root/.cache/restic
    entrypoint: ["/bin/sh", "-c"]
    # Runs the backup on container start, then repeats every 24 hours
    command:
      - |
        while true; do
          /usr/local/bin/backup.sh
          echo "Sleeping for 24 hours until next scheduled backup..."
          sleep 86400
        done

volumes:
  # Declare external volumes that exist on your host
  openwebui_data:
    external: true
  ollama_data:
    external: true
  caddy_data:
    external: true
Step 5: Executing the Initial Backup & Verification
Launch the backup container to initiate your first snapshot:
docker compose up -dInspect the container logs to watch the encryption, chunking, and upload process:
docker compose logs -f restic-backupNotice the power of deduplication: while raw data may total 15+ GB across multiple services, Restic transmits only unique encrypted blobs to your S3 bucket.
Step 6: Listing and Inspecting Snapshots
To inspect your backup history at any time without downloading files, execute the snapshots command within the container:
docker compose exec restic-backup restic snapshotsRestic displays a clean tabular overview of all point-in-time states:
ID        Time                 Host        Tags                      Paths
----------------------------------------------------------------------------
8f3c2a1b  2026-09-28 18:30:12  prod-srv-1  docker-volumes,host-prod  /data
c4d1e9f0  2026-09-27 18:30:15  prod-srv-1  docker-volumes,host-prod  /data
----------------------------------------------------------------------------
2 snapshots
Step 7: Disaster Recovery: Restoring Volumes
Backups are meaningless if you cannot restore them quickly during an emergency. To restore a volume snapshot onto a clean server or recovered volume:
1. Identify the target snapshot ID using restic snapshots.
2. Execute the restore command into a recovery directory:
docker compose exec restic-backup restic restore 8f3c2a1b --target /restoreTo restore a single specific volume (for instance, only your Caddy TLS certificates) without restoring the entire snapshot, use the --include filter:
docker compose exec restic-backup restic restore latest --target /restore --include /data/caddyHandling Live Databases (PostgreSQL / MySQL)
While Restic creates consistent filesystem snapshots, active ACID databases (such as PostgreSQL or MySQL) may hold unwritten transactions in memory. For mission-critical databases, implement one of two strategies:
- Database Dump Hook (Recommended): Before Restic runs, execute
docker exec db-container pg_dumpall -U postgres > /dump/db.sqland include the dump directory in your Restic snapshot path. - Container Freeze: Use
docker pause db-containerimmediately before the Restic backup anddocker unpause db-containerimmediately after. Because Restic’s snapshotting phase takes only a few seconds, database interruption is negligible.
Troubleshooting Common Restic Issues
1. Repository Lock Errors (unable to create lock in backend)
- Symptom: Backup fails with
unable to create lock in backend: repository is already locked. - Fix: This happens if a server rebooted or was forcefully terminated mid-backup. Clear stale locks with
docker compose exec restic-backup restic unlock.
2. S3 Authentication or Signature Errors
- Symptom: Output displays
SignatureDoesNotMatchorInvalidAccessKeyId. - Fix: Verify your
AWS_ACCESS_KEY_IDandAWS_SECRET_ACCESS_KEYin.env. For non-AWS providers like MinIO or Wasabi, ensure yourRESTIC_REPOSITORYstring includes the full URL protocol, e.g.,s3:https://s3.wasabisys.com/bucket-name.
Conclusion
Automating your Docker volume backups with Restic and S3 storage gives your infrastructure true enterprise resilience. With automated deduplication drastically lowering your S3 storage bill and military-grade client-side encryption protecting every byte, you can rest easy knowing your container fleet is protected against server crashes, accidental deletion, and ransomware.

Hi, I’m Mark, the author of Clever IT Solutions: Mastering Technology for Success. I am passionate about empowering individuals to navigate the ever-changing world of information technology. With years of experience in the industry, I have honed my skills and knowledge to share with you. At Clever IT Solutions, we are dedicated to teaching you how to tackle any IT challenge, helping you stay ahead in today’s digital world. From troubleshooting common issues to mastering complex technologies, I am here to guide you every step of the way. Join me on this journey as we unlock the secrets to IT success.